
PersonalDataProtection.
We bring your company into compliance with the Organic Law on Personal Data Protection (LOPDP): data inventory, legal bases, policies, contracts, a data protection officer (DPO) and data breach response, explained in clear language for your team.
Your clients' and employees' data is trust they placed in you. Protecting it is not just about complying with a law: it is about protecting the reputation your company has built over the years.
Six steps to comply with the law.
We implement data protection in your company as a structured program, with concrete deliverables at each stage and clear ownership.
- 01Understand
Data inventory
We identify what personal data your company processes, where it comes from, where it is stored and who it is shared with.
- Processing map
- Sensitive data
- Data flows and third parties
- 02Establish
Legal bases and consent
We define the legal basis for each processing activity and review how consent is obtained and documented.
- Lawful bases
- Forms
- Consent records
- 03Inform
Policies and notices
We draft your privacy policy, notices and clauses for clients, employees and suppliers.
- Privacy policy
- Notices and clauses
- Internal policy
- 04Secure
Security and processors
We review security measures and the contracts with suppliers that process data on your company's behalf.
- Data processor agreements
- Security measures
- International transfers
- 05Respond
Data subject rights
We put in place a procedure to respond on time to access, rectification, erasure and objection requests.
- Response procedure
- Deadlines and formats
- Request log
- 06Respond
Breaches and audits
We prepare your incident response protocol and periodically review that the program remains up to date.
- Incident protocol
- Notification to the authority
- Periodic audits
Privacy, done right.
We support companies across all industries, from the initial assessment to the day-to-day management of data protection.
- Compliance
- 01
Assessment and compliance plan
- 02
Policies, notices and contracts
- Management
- 03
Data protection officer (DPO)
- 04
Impact assessments
- Response
- 05
Security breaches
- 06
Inquiries and proceedings
Assessment and compliance plan
We assess your company's level of compliance with the law and deliver a prioritized plan with deadlines and owners.
- Compliance gaps
- Prioritized plan
- Timeline
Policies, notices and contracts
We prepare the documentation the law requires: policies, privacy notices, clauses and contracts with data processors.
- Privacy policy
- Supplier contracts
- Employment clauses
Data protection officer (DPO)
We advise on the appointment of your data protection officer (DPO) and support them in carrying out their duties.
- Appointment
- Ongoing support
- Reports to management
Impact assessments
We analyze higher-risk processing, such as sensitive data, profiling or video surveillance, and define measures to reduce that risk.
- Sensitive data
- New technologies
- Mitigation measures
Security breaches
When an incident occurs, we assess it with you, coordinate notification to the authority and to data subjects, and document every step.
- Incident assessment
- Notifications
- Remediation plan
Inquiries and proceedings
We represent your company before the data protection authority and in complaints filed by data subjects.
- Requests from the authority
- Data subject complaints
- Defense in proceedings
What the law requires of you today.
The Organic Law on Personal Data Protection (LOPDP) is in force, and the Superintendency of Data Protection is responsible for enforcing it. These are the obligations we review at every company.
A data protection program for a logistics and import company.
We led the implementation of a data protection program for a major logistics and import company, which now complies with the regulations and better protects its clients' information.
Data protection officer
Appointment where the law requires it.
Record of processing
What data you process and why.
Impact assessment
For high-risk processing.
Breach notification
To the authority and data subjects, on time.
Transfers
Sending data to other countries.
Data subject rights
Access, rectification, erasure and more.
Security
Technical and organizational measures.
Consent
Clear, informed and demonstrable.
One team, one point of contact.
Initial meeting
We listen to your situation in full confidence and review the information available.
Assessment
We identify risks, outstanding obligations and priorities for your company.
Plan and budget
We propose the roadmap, timeline and team, including any other practice areas of the firm that need to be involved.
Execution and follow-up
A lead lawyer coordinates everything and keeps you clearly informed at every step.
Six consecutive years in Band 1.
Leaders League has ranked Fexlaw in the top band for Criminal Law and Compliance in Ecuador for six years running. Chambers and Partners and the intellectual property rankings also recognize us for our anti-piracy work.
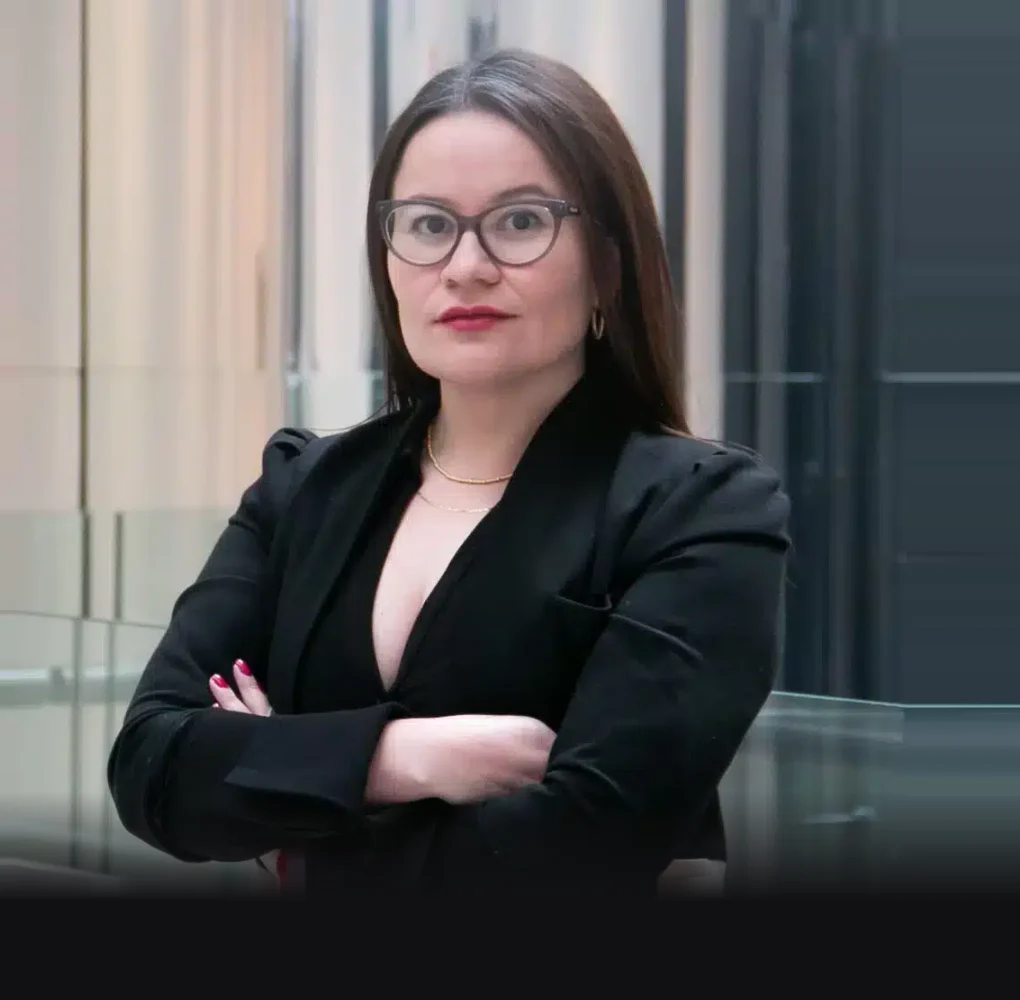
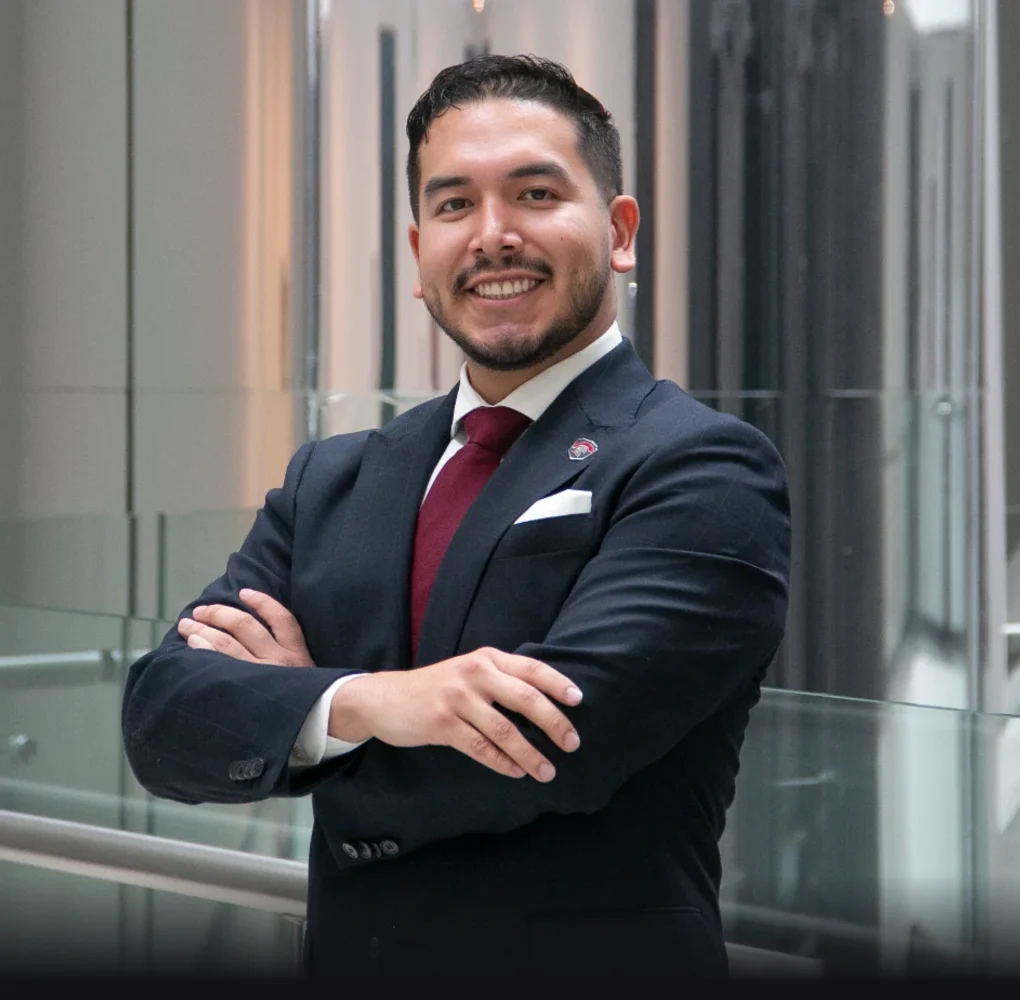
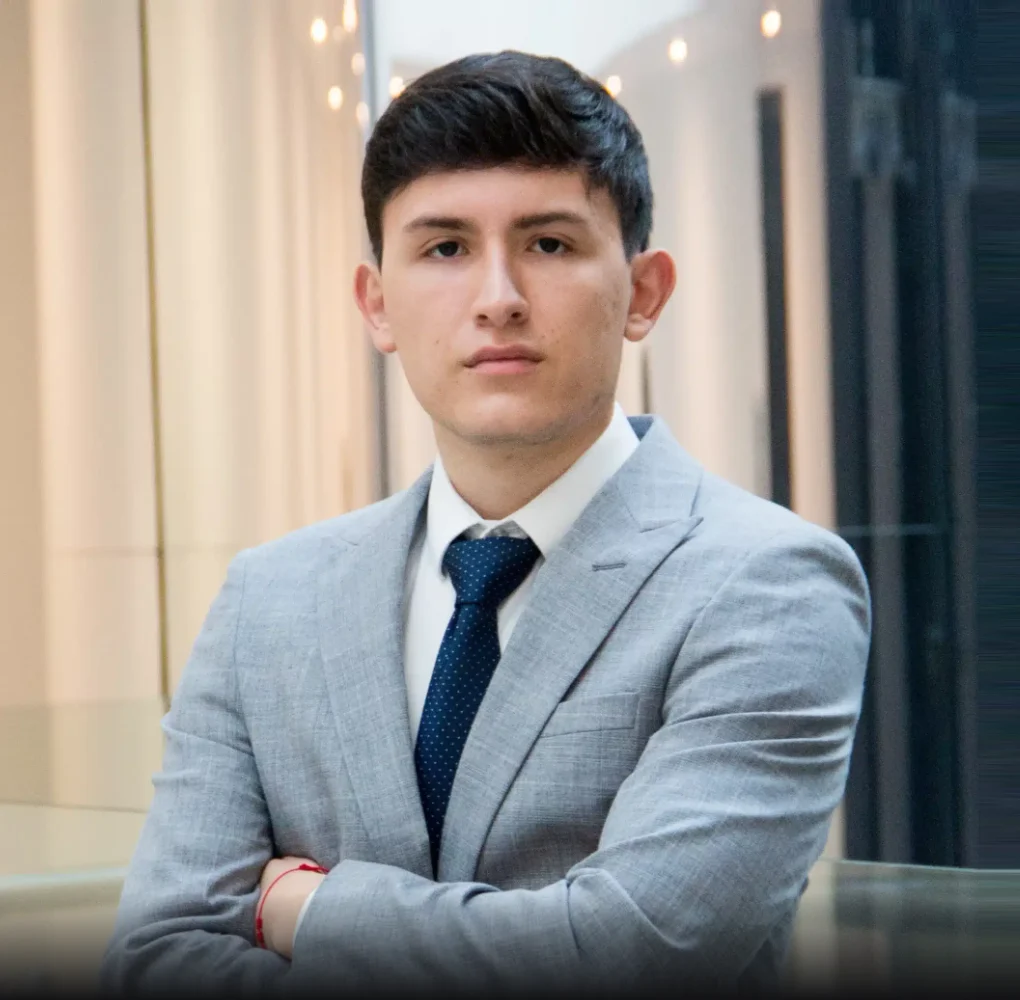
The people behind behind your compliance.
Lawyers who combine data protection, corporate and employment law, with the experience of having implemented the program at our own firm.
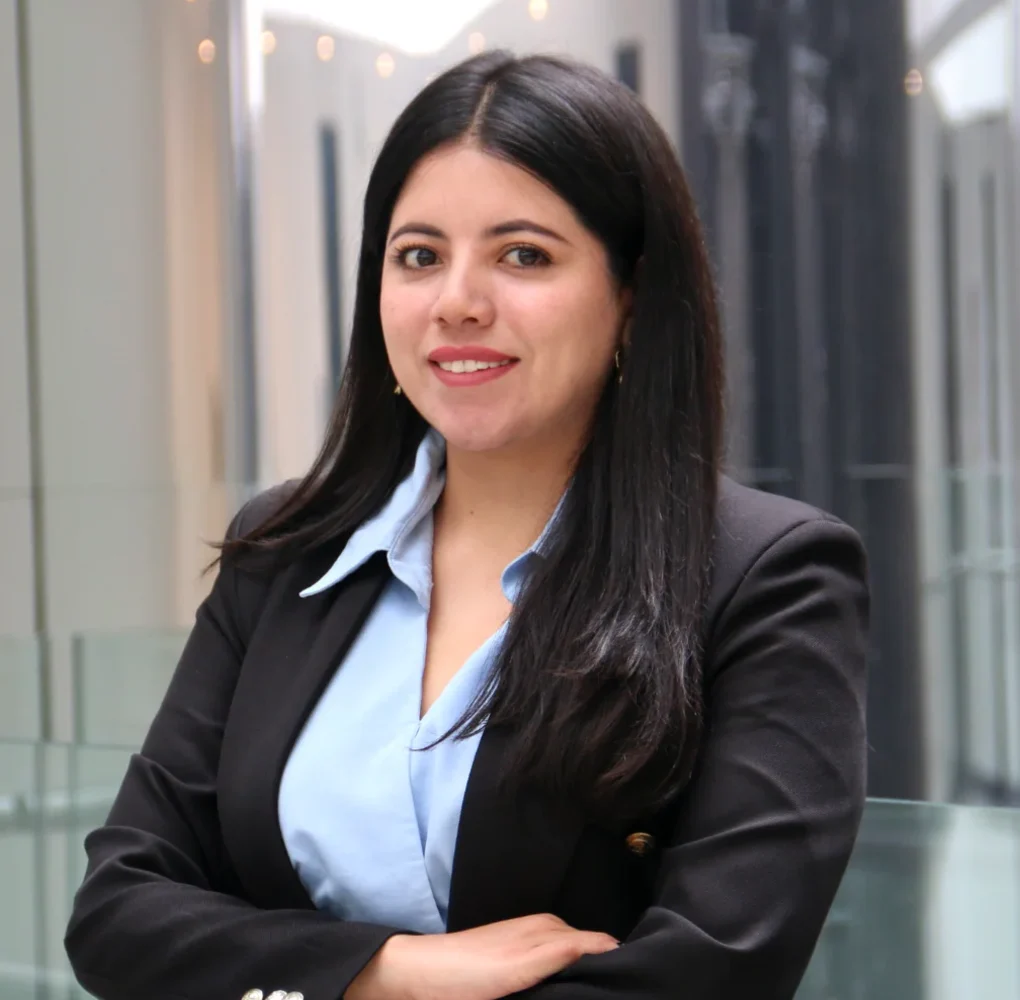 Practice lead
What clients often ask us.
General answers to common questions. Every company is different: write to us so we can review your situation.
01Which companies must comply with the data protection law?
Every company that processes personal data of clients, employees or suppliers in Ecuador, regardless of size. The specific obligations depend on the type and volume of data it handles.
02What is a data protection officer (DPO)?
The person who oversees compliance with the law within the organization and serves as the point of contact with the authority. The law sets out the cases in which appointing one is mandatory.
03What happens if my company suffers a data breach?
You must assess the incident, contain it and, where applicable, notify the authority and the affected individuals within the legal deadlines. A protocol prepared in advance makes all the difference.
04What penalties does the law provide for?
The law provides for corrective measures and fines calculated based on the company's turnover, in addition to the reputational damage that non-compliance entails.
05Do I need consent for everything?
No. Consent is one of several legal bases; others include, for example, performing a contract or complying with a legal obligation. We define the right basis for each processing activity.
Let's talk about
your data.
Choose the option that best describes your situation and we will message you directly on WhatsApp to book a confidential initial meeting.
into data protection complianceBook via WhatsAppINCIDENTWe had a data breach or
a request from the authorityBook via WhatsApp
